For small and medium-sized businesses (SMBs), email is the backbone of daily operations, client negotiations, and financial transactions. However, email is also the primary vector for cyberattacks. Without robust authentication protocols, bad actors can forge your domain name, send convincing phishing emails to your customers, and severely damage your brand reputation.
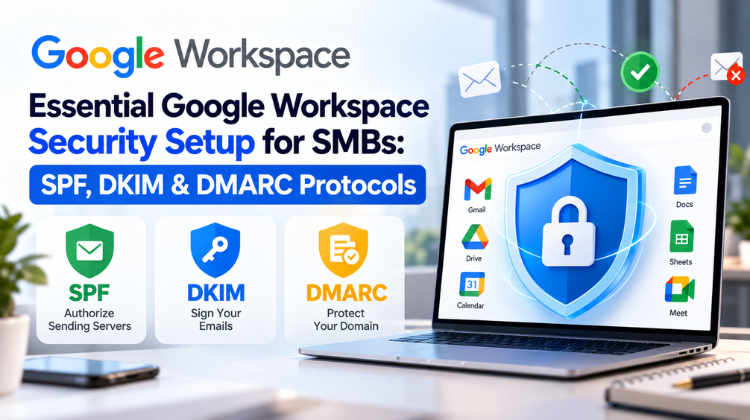
Implementing an Essential Google Workspace Security Setup for SMBs using Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), and Domain-based Message Authentication, Reporting, and Conformance (DMARC) is no longer optional. Search engine providers and major inbox gateways (including Google and Yahoo) mandate these protocols for sender verification.
In this comprehensive technical guide, we will walk through the exact steps to configure SPF, DKIM, and DMARC protocols within your DNS management console and Google Workspace Admin account to secure your domain, maximize inbox deliverability, and safeguard your business.
1. Why Email Security is Critical for Small Businesses
Small and medium-sized enterprises are frequently targeted by cybercriminals precisely because their IT security infrastructure is often less rigid than large enterprise setups. Common threats include:
Business Email Compromise (BEC): Fraudulent messages designed to trick employees or clients into transferring funds or revealing sensitive credentials.
Domain Spoofing: Attackers directly forge your @yourcompany.com email address in the From header field to send spam or malicious payloads.
Email Deliverability Failure: Major recipient gateways flag unauthenticated emails as spam or outright reject them, leading to missed sales leads and disrupted client communication.
By deploying a structured Google Workspace Security Setup for SMBs, you establish a multi-layered cryptographic defense that verifies sender identity and protects your domain authority across global mail networks.
2. Understanding the Email Authentication Triad: SPF, DKIM & DMARC
To configure your security settings correctly, it is important to understand how these three standards interact:
Sender Policy Framework (SPF)
SPF is a domain-level policy record published in your DNS that lists all IP addresses and third-party host servers authorized to send outbound emails on behalf of your domain name. When a recipient server receives an email from your domain, it checks your SPF record to verify whether the originating server’s IP address is listed.
DomainKeys Identified Mail (DKIM)
While SPF authenticates the sending server’s IP, DKIM secures the actual email contents using public-key cryptography. Google Workspace generates a private key to sign outbound messages automatically. The receiving email server retrieves your public key from your domain’s DNS records to verify that the message was signed by an authorized key and was not modified in transit.
Domain-based Message Authentication, Reporting & Conformance (DMARC)
DMARC links SPF and DKIM together by enforcing alignment between the visible From address and the authenticated sending domains. Additionally, DMARC instructs receiving mail servers on what actions to take if an email fails both SPF and DKIM checks—whether to accept it, move it to spam/quarantine, or block it entirely. DMARC also generates automated diagnostic reports sent back to your IT domain administrators.
3. Step 1: Configuring Sender Policy Framework (SPF) in Google Workspace
A proper Google Workspace Security Setup for SMBs begins with creating a valid SPF record in your DNS zone file.
Standard Google Workspace SPF Syntax
If Google Workspace is your sole outbound email provider, your DNS TXT record should be formatted as follows:
Host / Name: @ or leave blank depending on your DNS host (e.g., GoDaddy, Cloudflare, Namecheap).
Record Type: TXT
Record Value: v=spf1 include:_spf.google.com ~all
Critical Rules for SPF Records
Never Publish Multiple SPF Records: A domain name MUST have only one valid SPF record. Publishing multiple v=spf1 TXT records causes a permanent failure (PermError) on recipient servers.
Merging Third-Party Senders: If your small business sends bulk transactional or marketing emails via external platforms (such as Mailchimp, SendGrid, or Salesforce), merge those include mechanisms into a single SPF record string:
v=spf1 include:_spf.google.com include:servers.mcsv.net ~all
Respect the 10-DNS Lookup Limit: The SPF specification caps the number of domain-name lookups at ten. Going above this limit breaks SPF validation.
4. Step 2: Generating & Enabling DKIM Keys in Google Workspace
The second core element of an effective Google Workspace Security Setup for SMBs is activating DKIM cryptographic signing within your Google Admin Console.
Process to Generate and Activate DKIM Keys
Access Google Admin Console: Log in to your Google Admin Console as a Super Administrator.
Navigate to Email Authentication: Go to Apps > Google Workspace > Gmail > Authenticate email.
Select Domain & Generate Key: Choose your primary business domain name from the dropdown menu and click Generate New Record.
Choose Key Settings:
Copy DNS Values: The console displays a DNS Host name (e.g., google._domainkey) and a long TXT record value starting with v=DKIM1; k=rsa; p=....
Publish to DNS: Access your domain registrar or DNS management dashboard, create a new TXT record, paste the host name and key value, and save changes.
Start Authentication: Return to the Google Admin Console and click Start Authentication.
5. Step 3: Implementing DMARC Policies & Diagnostic Reporting
With SPF and DKIM records published, the final phase of a complete Google Workspace Security Setup for SMBs is defining your DMARC policy.
Formulating Your DMARC TXT Record
DMARC records are published as TXT records under the host name _dmarc.yourdomain.com.
Phase 1: Monitoring Policy (Recommended Starting Point)
When deploying a Google Workspace Security Setup for SMBs, start with a monitoring policy (p=none) to review diagnostic aggregate reports without impacting legitimate email traffic:
Phase 2: Quarantine Policy
After reviewing reports and verifying that all legitimate email flows pass SPF and DKIM alignment checks, update your policy to quarantine unauthorized emails:
Phase 3: Reject Policy (Maximum Security)
Once your email ecosystem is fully validated, enforce strict blocking to instruct remote mail servers to reject non-aligned messages outright:
6. Advanced Admin Safeguards Beyond Email Protocols
While SPF, DKIM, and DMARC form the cornerstone of email authentication, a holistic Google Workspace Security Setup for SMBs requires hardening administrative and account security settings directly within the Google Workspace Admin Console:
Enforce 2-Step Verification (2SV): Mandate 2-Step Verification across all user accounts, restricting the use of weak SMS verification in favor of authenticator apps or hardware security keys.
Restrict Third-Party API Access: Audit and limit OAuth application access to prevent malicious third-party apps from reading emails or accessing Google Drive contents.
Configure Data Loss Prevention (DLP): Set up rules to detect and block sensitive content (such as credit card numbers, tax IDs, and confidential internal files) from being emailed externally.
Outbound Phishing Protection: Enable aggressive spam and phishing filters in Google Workspace Gmail settings to identify spoofed internal display names.